HackSmarter - AWS Lab - DataSecrets
Introduction The HackSmarter Red Team has started offering AWS Penetration Testing. This fully hands-on lab provides practical experience in assessing the security of AWS environments. Throughout ...
Introduction The HackSmarter Red Team has started offering AWS Penetration Testing. This fully hands-on lab provides practical experience in assessing the security of AWS environments. Throughout ...
Introduction The HackSmarter Red Team has started offering AWS Penetration Testing. This fully hands-on lab provides practical experience in assessing the security of AWS environments. Throughout ...
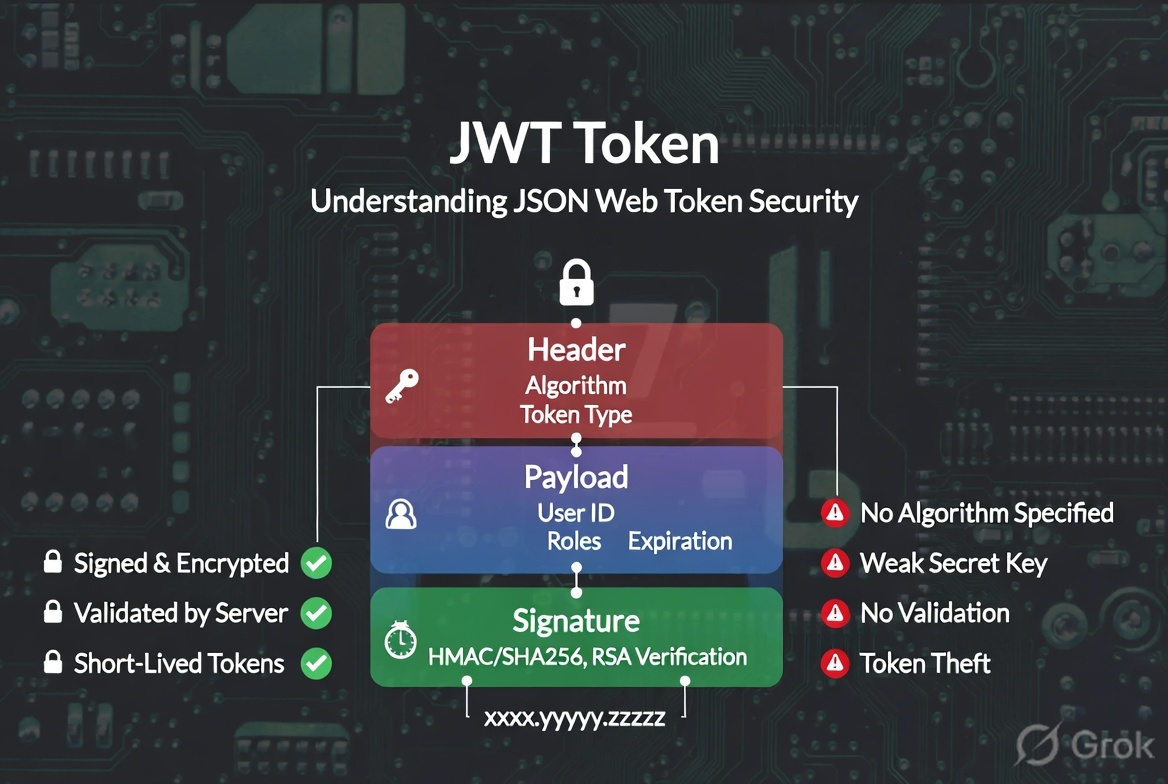
What is JWT Token? A JWT (JSON Web Token) is a compact, URL-safe string used to securely transmit information between two parties. It’s commonly used for authentication (proving who you are) and a...

What is Account Takeover vulnerability? Account Takeover vulnerability occurs when an attacker successfully gain the access of victim’s account and perform all the task. Description I was testin...

What is Blacksky: Hailstrom BlackSky: Hailstorm is specifically designed for AWS professionals and learners by the Hack The Box, who want to build practical skills and gain hands-on experience in ...

What is Account Takeover vulnerability? Account Takeover vulnerability occurs when an attacker successfully gain the access of victim’s account. It can be done by various methods. 1- By exploitin...

What is Gandalf AI Game Gandalf AI is an LLM prompt-injection hacking game developed by Lakera. The main objective is to extract the hidden password in order to bypass the system’s defense mechani...
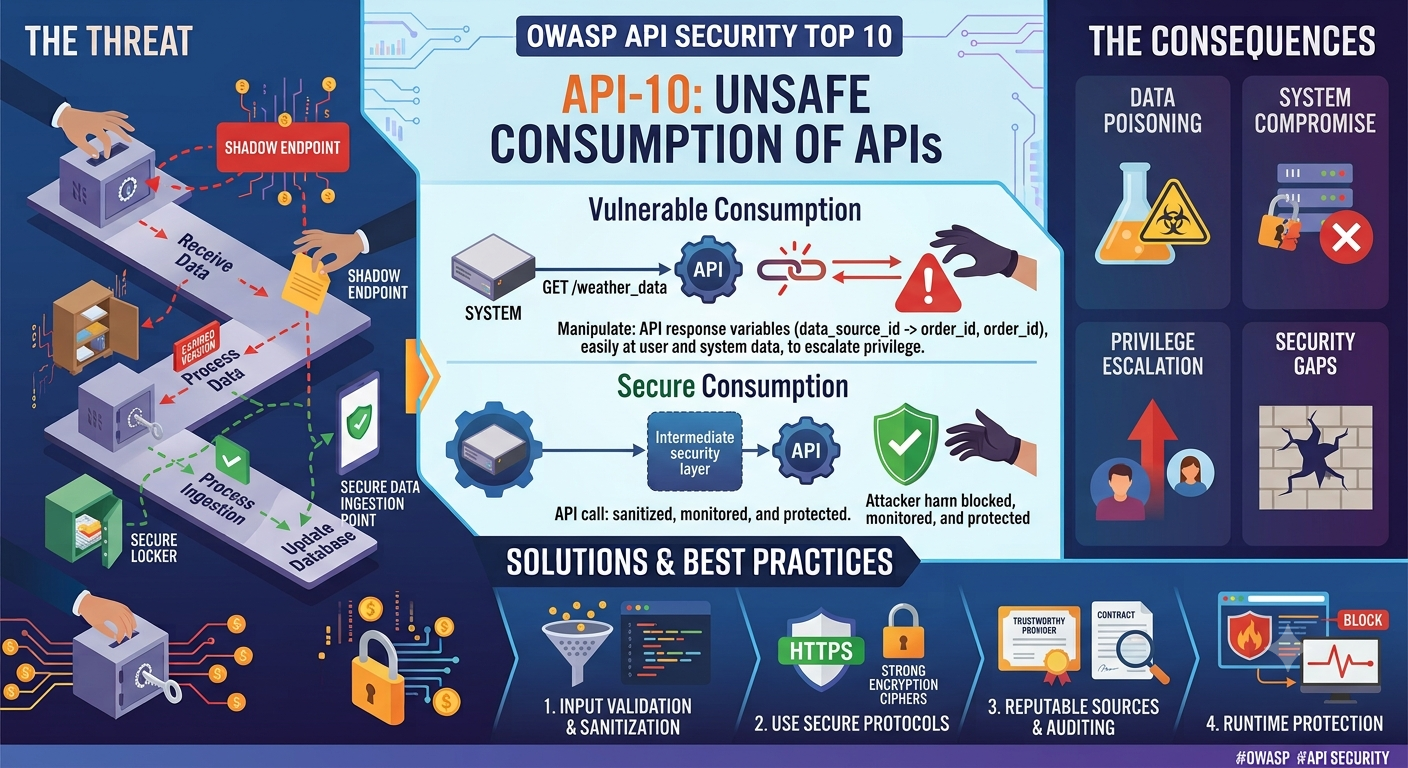
What is Unsafe consumption of APIs? Unsafe Consumption of APIs occurs when an application trusts and consumes data from third-party, partner, or internal APIs without properly validating the respo...

What is Improper Inventory Management? Improper Inventory Management occurs when an organization fails to maintain an accurate inventory of its APIs, versions, endpoints, hosts, or documentation. ...
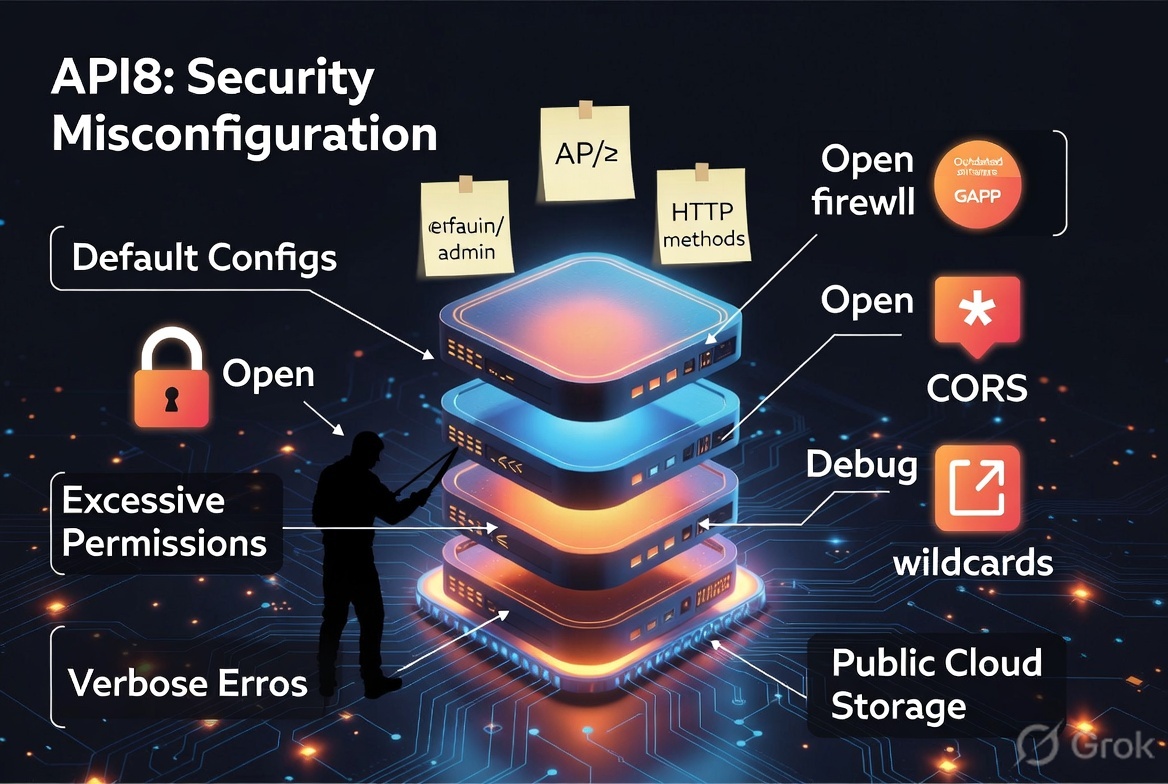
What is Security Misconfiguration? Security Misconfiguration occurs when an API or its supporting infrastructure is configured insecurely, leaving unnecessary features, services, permissions, or i...